About Prep4sures Splunk SPLK-3001 Exam
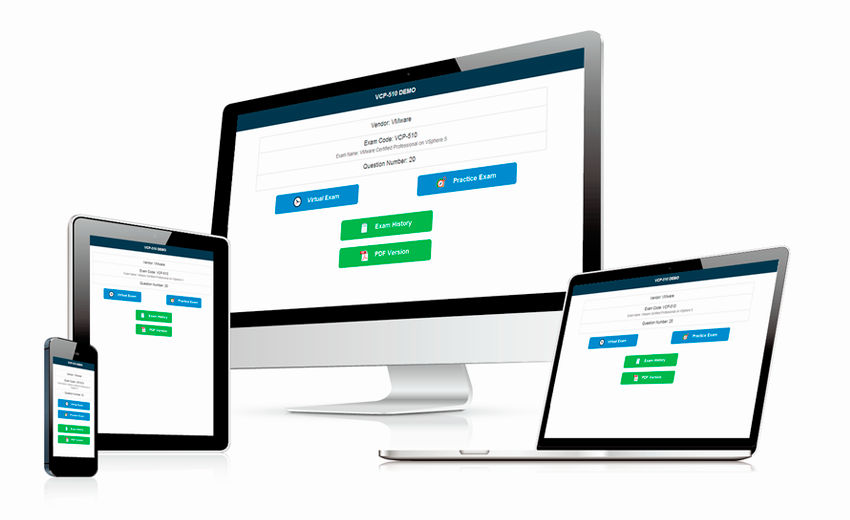
Self-Assessment & interactive experience - Splunk Enterprise Security Certified Admin Exam online test engine
You can simply trust our products to help you ride smoothly through your Splunk Enterprise Security Certified Admin actual exams. Our Splunk Enterprise Security Certified Admin Exam online test engine can give you special practice experience for your preparation. You can customize your exam based on your objectives. When you choose our Splunk Enterprise Security Certified Admin Exam online test engine, the modern and user friendly interface will give you surprise and motivate your enthusiasm for the SPLK-3001 study preparation. Besides, you can do seft-assessment after each time of practice test. You will get a test score after completing the Splunk Enterprise Security Certified Admin Exam prep practice. The contents of SPLK-3001 online test engine are compiled by our professional expert team and each questions from it is selected and verified according to strict standards, which can ensure you pass at first attempt and get high scores.
Dear everyone, do you still find the valid study material for SPLK-3001 certification? Maybe, you have been confused by various website and Splunk Enterprise Security Certified Admin Exam prep study material. How to distinguish it is valid or not is a difficult thing. Now, we will recommend our Splunk Enterprise Security Certified Admin Exam easy download preparation to all of you. Our SPLK-3001 sure pdf prep is designed specially to all of the IT candidates and to ensure the optimum performance. Additionally, our Splunk Enterprise Security Certified Admin Exam vce prep torrent are compiled and verified to guarantee you to learn the exact information which will in your actual test. So, with the Splunk Enterprise Security Certified Admin SPLK-3001 valid free torrent, you will not waste precious studying time filling your head with useless information. You will pass your real test at your first attempt with our Splunk Enterprise Security Certified Admin Exam latest prep dumps.

Free update for one year & Full refund policy
Our goal is to help you pass, so the Splunk Enterprise Security Certified Admin Exam prep study material you get is the best study training material which edited and made by our professional experts with lots efforts. When you buy our SPLK-3001 sure pdf prep, we can ensure it is the latest and best valid study material for your preparation. You do not worry it is update just after your purchase, because we provide one year free update after you complete the purchase of Splunk Enterprise Security Certified Admin Exam latest prep dumps. Our system will send the latest Splunk SPLK-3001 easy download preparation to your payment email as soon as the dump is updated. You can check your email for the update or check the version No. on our product page. If the version number is increased, the Splunk Enterprise Security Certified Admin Exam prep study material is updated. So when you have more access to our latest exam study material rather than the less update time from other vendors.
In addition, we will provide a full refund in case of failure. Although we promise our Splunk Enterprise Security Certified Admin Exam latest prep dumps will successfully help you 100% pass, there are many uncertain factors which will affect your Splunk Enterprise Security Certified Admin actual test, so we provide the refund policy to ensure your benefits. You just need to show us your screenshot of failure Splunk Enterprise Security Certified Admin Exam certification. Besides, our policy is based on open communication and trust with our customers. We are more than just an exam dump provider, we are your guides to a passing score, and we are always here to help you.
Instant Download: Our system will send you the SPLK-3001 braindumps files you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
What skills and knowledge would you gain from a Splunk SPLK-3001?
The SPLK-3001 will develop your skills to the next level with regard to data analysis, software architecture and databases. With this certification, you'll gain the following skills:
Many days of learning regarding how Hadoop works and how it can be integrated into your database.
The fundamental knowledge of how to design and set the architecture for a Splunk Enterprise deployment.
There are many advantages that you can get from becoming a certified Splunk SPLK-3001. The most important advantage is the assurance of benefits from your employer. So if you have a Splunk SPLK-3001 certification, employers expect you to be able to understand complex information quickly and accurately.
In addition, a Splunk SPLK-3001 certification will help you in quickly grabbing the attention of potential clients and employers. This certification indicates that you are not only experienced in Splunk, but also in all other aspects of the software industry. These employers will certainly make you an attractive candidate for their hiring needs.
There you can get information about the Difficulty in writing the Splunk SPLK-3001 Exam
There are great deals of problems a Possibility faced when Potential consumers begin preparing yourself for the Splunk SPLK-3001 Exam. If a possibility plans to prepare his for the Splunk SPLK-3001 Examination with no issue along with in a similar means obtain superior premium quality in the. After that they call for to select the best Splunk SPLK-3001 unloads real issues approach. There are lots of web net sites that are supplying one of the most existing Splunk SPLK-3001 Examination problems together with responses yet these concerns are not validated by Microsoft identified professionals which's why various are fallen short in their simply preliminary effort. Prep4sures is the straight-out outstanding platform which uses the possibility with the essential Splunk SPLK-3001 concerns that will most absolutely help him to pass the Splunk SPLK-3001 on the very truly very first time. The possibility will certainly most absolutely not need to take the Splunk SPLK-3001 exam 2 times as a result of the reality that with the help of the Splunk SPLK-3001 Dumps Possibility will definitely have every important item called for to pass the Splunk SPLK-3001 Test. We are supplying among the most about day together with authentic questions which is the variable that this is the one that he requires to profit from in addition to there are no chances to stop working when a prospect will most definitely have reputable mind tosses out from Prep4sures. We have the assurance that the problems that we have will definitely be the ones that will definitely pass possibility in the Splunk SPLK-3001 Examination in the as a matter of fact incredibly initial campaign.
Reference: https://www.splunk.com/en_us/pdfs/training/splunk-test-blueprint-es-admin.pdf
Certification Topics of Splunk SPLK-3001 Certification Exam
Our Splunk SPLK-3001 exam dumps covers the following objectives of Splunk SPLK-3001 Exam. The topics covered in the SPLK-3001 certification exam are:
Creating Correlation Searches 10%
Custom Add-ons 5%
Forensics, Glass Tables, and Navigation Control 10%
Validating ES Data 10%
Tuning Correlation Searches 10%
Threat Intelligence Framework 5%
ES Deployment 10%
Installation and Configuration 15%
Monitoring and Investigation 10%
Lookups and Identity Management 5%
Security Intelligence 5%
ES Introduction 5%
What is the validity of the SPLK-3001 Certification Exam
The SPLK-3001 certification will be valid for a year and must be renewed every year to keep them current with the technology changes in Splunk. The earliest you can renew your SPLK-3001 certification is March 1 of each year.
Splunk SPLK-3001 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Security Monitoring and Investigation | 10% | - Security posture analysis - Notable events and Incident Review |
| Topic 2: Data Validation & CIM | 10% | - Common Information Model (CIM) usage - Data normalization and validation |
| Topic 3: Splunk Enterprise Security Architecture & Deployment | 10% | - Distributed Splunk environment considerations - Enterprise Security deployment planning |
| Topic 4: Installation and Configuration | 15% | - Managing ES configuration and system health - Installing and upgrading Splunk Enterprise Security |
| Topic 5: Advanced ES Operations | - Correlation searches - Threat intelligence framework integration - Dashboards (Security Posture, Glass Tables, Investigations) - Risk-Based Alerting (RBA) |
Splunk Enterprise Security Certified Admin Sample Questions:
A set of correlation searches are enabled at a new ES installation, and results are being monitored. One of the correlation searches is generating many notable events which, when evaluated, are determined to be false positives.
What is a solution for this issue?
- A. Suppress notable events from that correlation search.
- B. Modify the correlation schedule and sensitivity for your site.
- C. Change the correlation search's default status and severity.
- D. Disable acceleration for the correlation search to reduce storage requirements.
Correct Answer: B 🗳️
Explanation: Only visible for Prep4sures members. You can sign-up / login (it's free).
Which of the following threat intelligence types can ES download? (Choose all that apply.)
- A. VulnScanSPL
- B. Text
- C. STIX/TAXII
- D. SplunkEnterpriseThreatGenerator
Correct Answer: C 🗳️
Explanation: Only visible for Prep4sures members. You can sign-up / login (it's free).
To which of the following should the ES application be uploaded?
- A. The search head.
- B. The KV Store.
- C. The indexer.
- D. The dedicated forwarder.
Correct Answer: A 🗳️
Explanation: Only visible for Prep4sures members. You can sign-up / login (it's free).
Which of the following are examples of sources for events in the endpoint security domain dashboards?
- A. Workstations, notebooks, and point-of-sale systems.
- B. Investigation final results status.
- C. Lifecycle auditing of incidents, from assignment to resolution.
- D. REST API invocations.
Correct Answer: A 🗳️
Explanation: Only visible for Prep4sures members. You can sign-up / login (it's free).
Why is data model acceleration important in Splunk Enterprise Security deployments?
- A. Encrypts indexed security data before replication between clustered enterprise indexers automatically.
- B. Improves search performance using summarized datasets generated from accelerated data models.
- C. Generates automatic remediation scripts responding to malware-related notable security incidents immediately.
- D. Synchronizes user authentication across distributed search head cluster member environments securely.
Correct Answer: B 🗳️
Explanation: Only visible for Prep4sures members. You can sign-up / login (it's free).
Viewing page 1 out of 24 pages.
Viewing questions 1-5 out of 118 questions.


 Alva

 Herman

 Bowen
 Juliet
 Claude
 Burnell
 Bevis
 Larry
 Alfred

 Porter
 Prima
 Adam
 Vita
 Alston
 Burke
 Althea
 Eugene
 Len
 Elton
 Jacob
 Judy